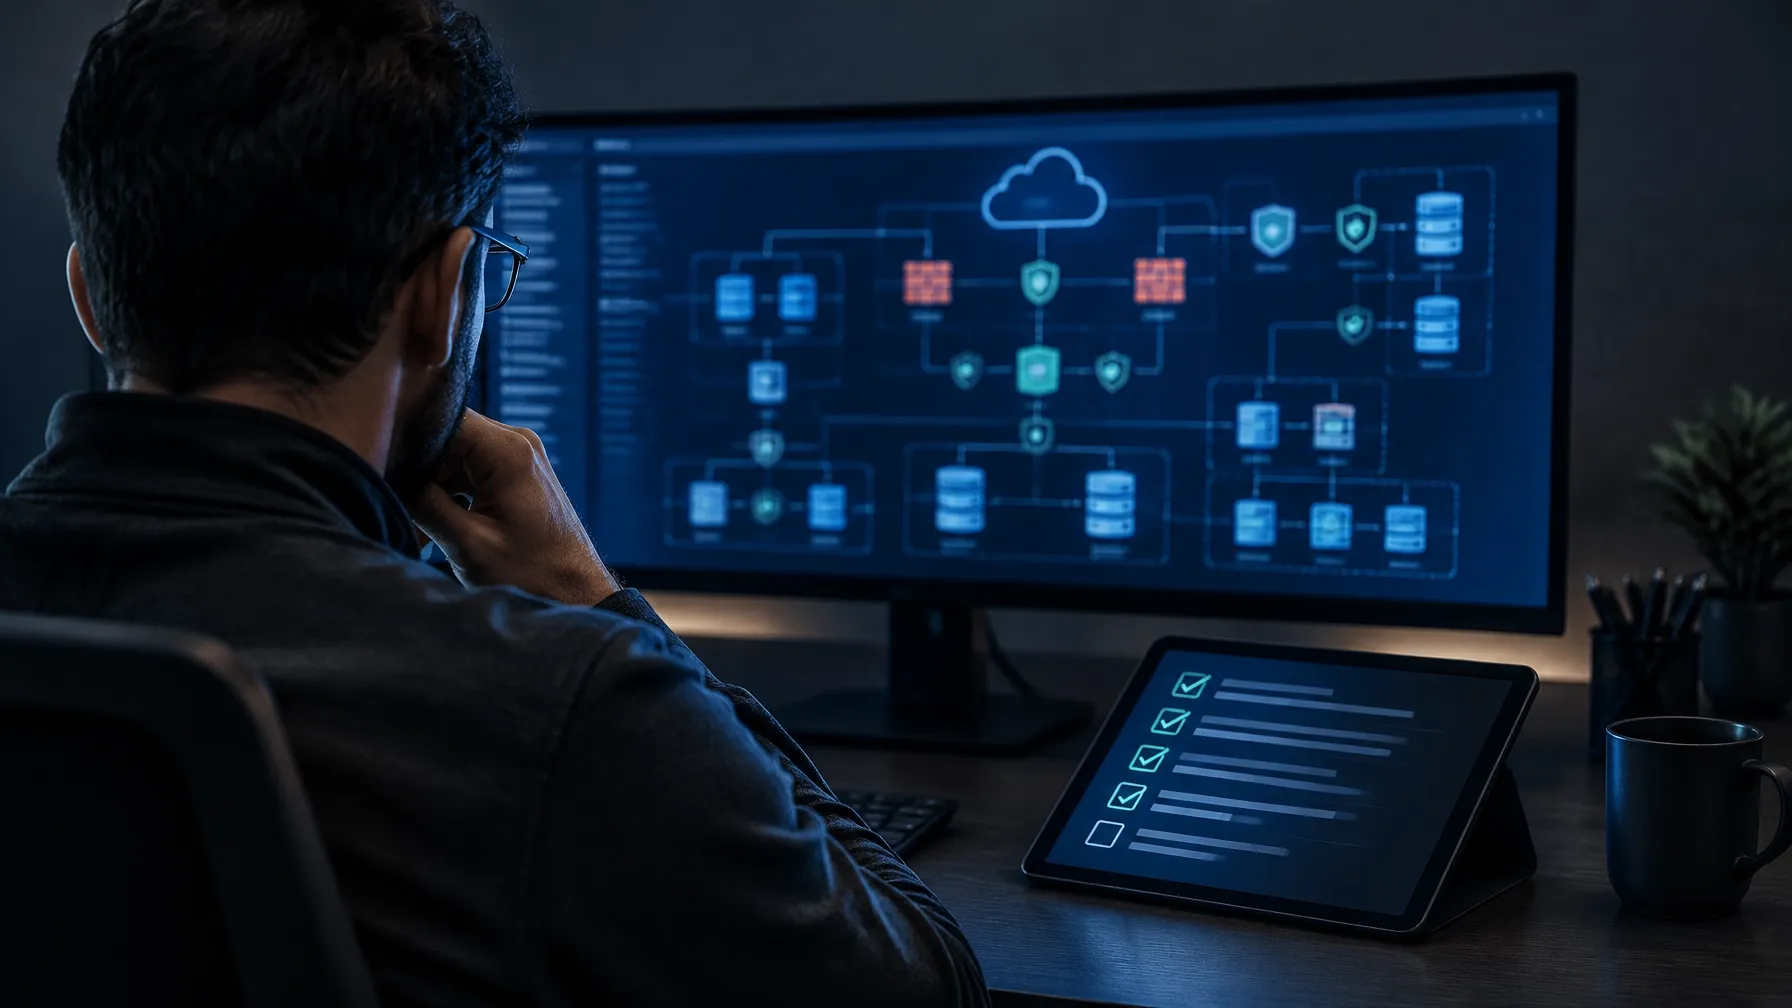
Cloud Security Posture Management (CSPM) gives a business a structured way to look for misconfigurations across cloud accounts, services and workloads. The practical value is not a dashboard by itself; it is making the gap between the intended configuration and the current environment visible to the people who can address it.
For a UK SME, a useful first pass should define the cloud environments in scope, the people responsible for them and the risks that matter most. Common questions include whether storage is exposed, whether access is broader than it needs to be, whether security settings are consistent and whether remediation work is tracked to completion. A CSPM process can help prioritise those questions rather than relying on occasional manual checks.
The often-quoted £15k annual saving should be treated as a prompt to investigate avoidable rework, exposure and operational effort, not as a guaranteed result. The actual value depends on the estate, current controls, internal capacity and the scope of the chosen service. Buyers should confirm coverage, integrations, alert handling, remediation workflow, data handling and commercial terms before selecting a product.
A practical evaluation asks for a clear demonstration of how the tool identifies a misconfiguration, explains its significance, assigns ownership and records remediation. It should also fit the organisation’s operating model. General information is not a substitute for advice on a customer’s specific security, contract or procurement context.